Letting users trust their own MCP clients, without opening a phishing hole
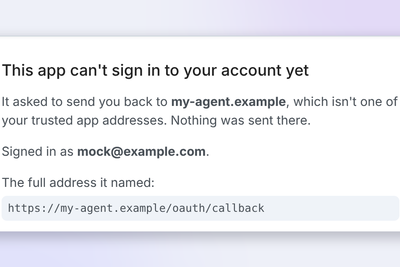
MCP servers face a security dilemma: they must either restrict redirect URIs to an allowlist to prevent phishing attacks where attackers steal user credentials, or accept any URI and risk being exploited. A May 2026 study found that 95.8% of tested MCP servers accept arbitrary redirect URIs, allowing attackers to register fake clients and intercept authorization codes to gain unauthorized access to users' storage buckets through a single deceptive link.